The BASE Group recognizes its responsibilities and role as a platform provider of payment and financial services open to society. To remain a trusted corporate group and fulfill our responsibilities to society, we recognize all information assets handled in our business activities as important management resources and information security as a key management priority. We hereby establish the following basic policy and declare our commitment to ensuring and continuously improving information security.
Establishment of and Compliance with Information Security Rules
The BASE Group establishes rules, including regulations, guidelines, and manuals, to protect information assets and ensures that they are thoroughly communicated to all employees and other relevant personnel, including temporary agency workers, contract employees, part-time employees, and business partners.
Establishment of an Information Security Management Framework
The BASE Group appoints an officer responsible for promoting information security to oversee and comprehensively manage information security, and establishes a framework for cooperation among the relevant departments.
Management secures and provides sufficient resources to plan and implement information security measures, including risk management, across the organization. We clearly define reporting and communication arrangements and procedures for responding promptly to incidents to minimize damage, restore operations quickly, and prevent recurrence.
Information Security Education
The BASE Group regularly provides information security education and training to enhance the security awareness and knowledge of all employees. We regularly review the content in light of changes in society and technology to ensure that our awareness-raising activities remain effective.
Risk Assessment and Implementation of Countermeasures
We analyze and assess threats to information assets and implement appropriate countermeasures according to the risks identified. We take a comprehensive approach to information security through organizational, human, technological, and physical measures.
Continuous Improvement of Information Security Measures
We regularly evaluate the effectiveness of our information security management system and strive for continuous improvement.
Preservation and Protection of Information Assets
We implement the security measures necessary to maintain the confidentiality, integrity, and availability of all information assets owned or managed by the BASE Group, including electronic data, paper documents, IT infrastructure, networks, and equipment.
Management of Outsourced Service Providers
When outsourcing services, the BASE Group appropriately supervises service providers through checks at the time of selection and on a regular basis thereafter, and strives to ensure that they maintain a security level equal to or higher than ours.
In the event of an information leak or other incident, we promptly take action to prevent further damage, identify the cause, and implement measures to prevent recurrence.
Compliance with Laws and Regulations
The BASE Group complies with the requirements of applicable laws, regulations, and guidelines, including the Act on the Protection of Personal Information, and works to improve information security.
To prevent non-compliance with laws, regulations, and other relevant standards, we regularly collect information on amendments, review our internal rules, and ensure that changes are thoroughly communicated to all employees.
This policy applies to all employees of the BASE Group and all other parties who have access to the Group’s information assets. By complying with this policy and working to maintain and improve information security, we will uphold the trust placed in us by our customers and society.
Established in January 2025
Governance Structure
Information Security Committee
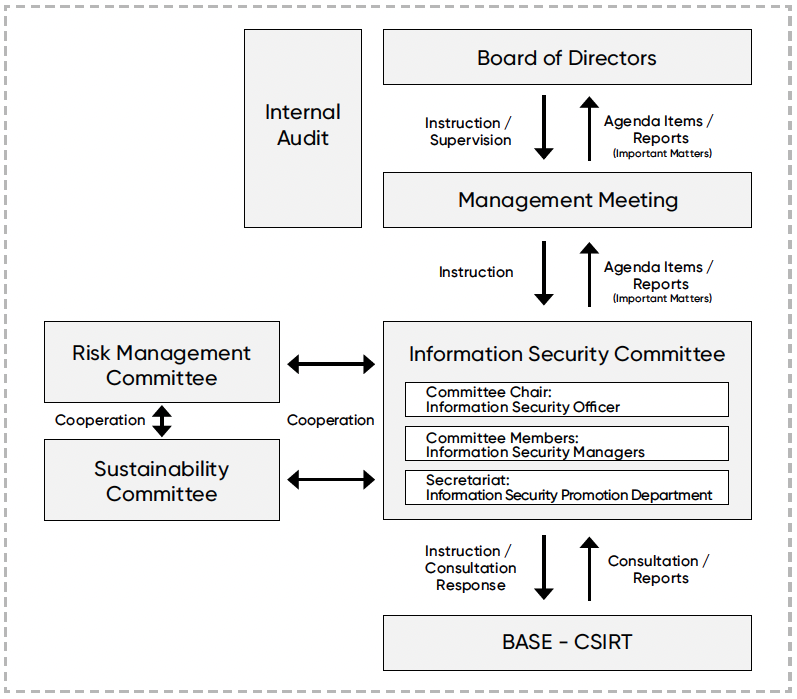
We have established an Information Security Committee, chaired by the Information Security Officer and composed of information security managers from each department, to promote and oversee information security initiatives company-wide.
Moreover, to implement effective security measures, we have established an Information Security Promotion Department that swiftly promotes and coordinates information security-related initiatives and plans.
Information Security Managers
The Company has appointed information security managers who are responsible for protecting and properly managing information assets, supporting officers and employees, and exercising comprehensive oversight of information security measures in each department.
BASE-CSIRT
BASE-CSIRT is the BASE Group’s internal CSIRT (Computer Security Incident Response Team). The team works in constant coordination across the Group to address issues, both in routine operations and in times of crisis.
Background to Its Establishment
As information security threats become more frequent and sophisticated, and as our services and workforce continue to expand, we established BASE-CSIRT to respond promptly to information security incidents and minimize damage. In May 2025, BASE-CSIRT joined the Nippon CSIRT Association.
https://www.nca.gr.jp/member/base-csirt.html
Activities
Serving under the Information Security Officer, BASE-CSIRT is composed mainly of security personnel selected from each department across the Group and an in-house security promotion team. The team investigates and analyzes potential issues to prevent incidents from occurring within the Group, shares risk information, and carries out incident response activities.
What Is a CSIRT?
CSIRT stands for “Computer Security Incident Response Team,” a specialized organization within a company or organization that responds to computer security incidents.
Organizational Chart
Initiatives to Enhance Security
Organizational Measures
Legal Compliance
We properly handle information assets in compliance with applicable laws, regulations, relevant standards, and contracts concluded with customers, business partners, and employees.
Continued Improvement
We respond to evolving risks and continuously improve information security by regularly reviewing and assessing our organizational and business risk responses.
Information Asset Management
We ensure and maintain the confidentiality, integrity, and availability of the information assets handled by the Company.
Response in Emergency Situations
In anticipation of potential disasters and other emergencies, we have established response procedures and frameworks to minimize the impact on our business and information security.
Management of Outsourced Service Providers
When outsourcing services, we appropriately supervise service providers through checks at the time of selection and on a regular basis thereafter, and strive to ensure that they maintain a security level equal to or higher than ours.
Handling of Personal Information
We are committed to implementing, strengthening, and upholding privacy measures to ensure that users can enjoy our services with peace of mind.
Refer to our Privacy Policy for details.
Human-level Measures
Non-disclosure Agreement
We have entered into non-disclosure agreements (NDAs) with all individuals directly employed by the BASE Group.
Improvement of Information Security Awareness
We provide information security-related education to all officers and employees on a regular basis.
Technological Measures
System Security Measures
We are committed to ensuring and enhancing security by formulating measures to prevent and prepare for various types of attacks, building organizational frameworks, and protecting information assets against all kinds of threats.
Vulnerability Assessment
We regularly conduct vulnerability assessments of our platforms and applications to detect potential vulnerabilities. Any vulnerabilities identified are remediated in accordance with our vulnerability management process.
Monitoring
We monitor for unauthorized access and various other events, and promptly respond when incidents with significant user impact are identified.
Physical Measures
Establishment of Security Perimeters
We establish physical security perimeters appropriate to the information assets being handled and monitor access accordingly.
Management of Information Terminals
Employees are provided with company-issued PCs equipped with the necessary security management tools and are required to perform their duties using these PCs.
Third-party Certification
To enable users to use our services safely and securely, the BASE Group has obtained security-related certifications from third-party organizations.
BASE, Inc., PAY, Inc., and want.jp Inc. have obtained certification to JIS Q 27001:2025 (ISO/IEC 27001:2022+Amd 1:2024), an international standard for information security management systems (ISMS), and have established and operate frameworks to ensure the confidentiality, integrity, and availability of information assets.
BASE, Inc. has obtained SAQ-A under PCI-DSS, the global security standard for the credit industry.
As PAY, Inc. and Estore Corporation hold credit card information, they manage such information in full compliance with PCI-DSS Version 4.0.1.